ニュー速+
1:
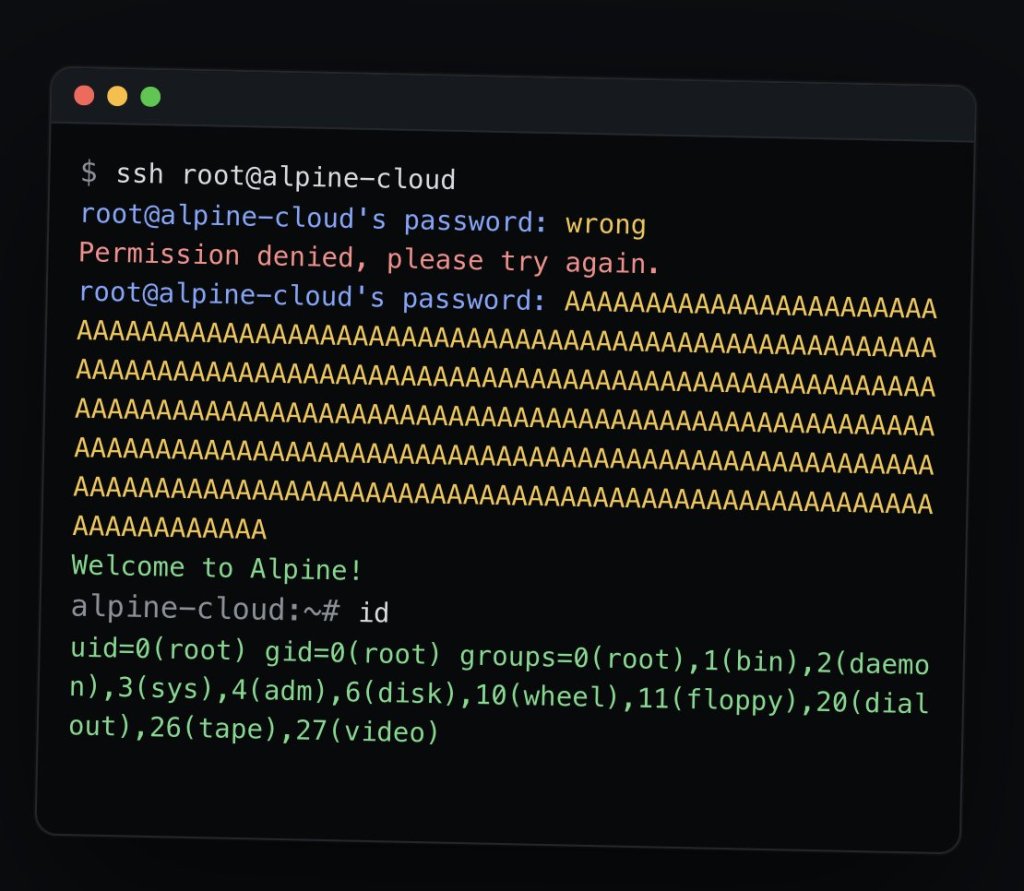
‼ 速報:OpenSSHが、攻撃者が適切なパスワードなしで一部のLinuxサーバーにログインできる重大な欠陥の修正を急いで公開しました。
チームはこのバグを1日前に知りました。OpenSSHのDamien Miller氏は、長い公開禁止期間は今や主に攻撃者を助けるだけで、AIエージェントがバグを再発見してしまうため、数時間以内にそれが起こることがあると述べています。
チームはこのバグを1日前に知りました。OpenSSHのDamien Miller氏は、長い公開禁止期間は今や主に攻撃者を助けるだけで、AIエージェントがバグを再発見してしまうため、数時間以内にそれが起こることがあると述べています。
‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password. The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours. It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY". Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.
— International Cyber Digest (@IntCyberDigest) November 5, 2026
2:
パスワードによる認証無効にしてりゃ防げるん?
3:
ほんと困るこれ
今も残業中
今も残業中